27 August 2026
Half of Queensland's independent schools do not enforce DMARC
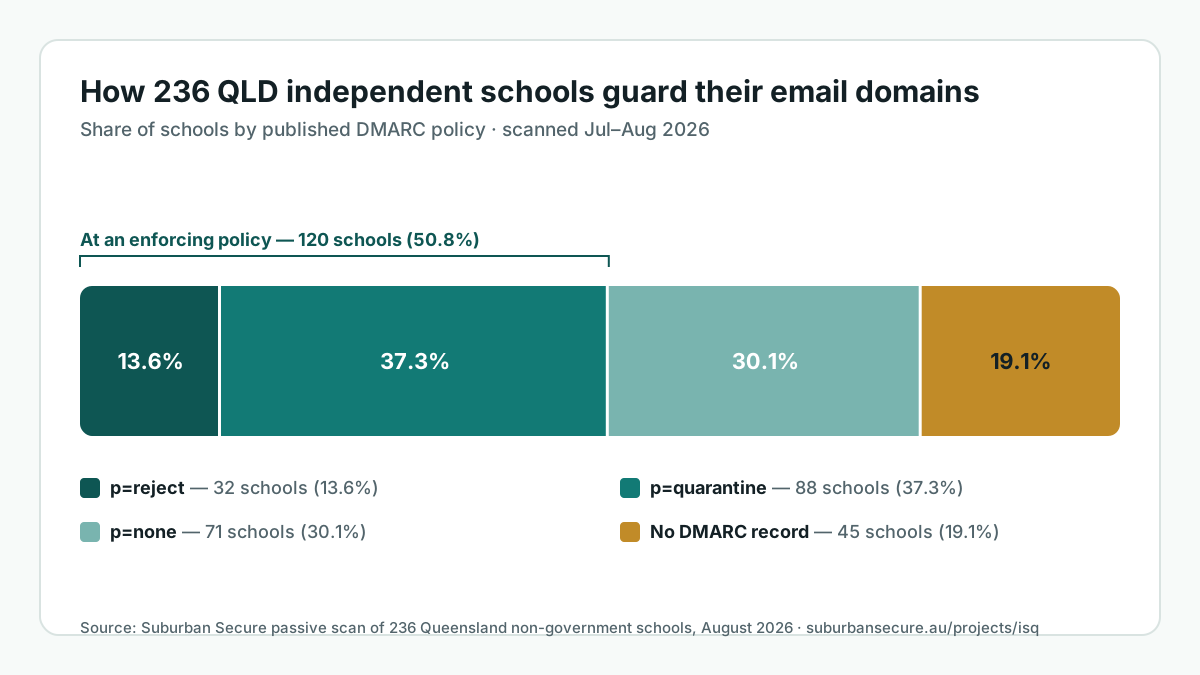
We scanned the public email-authentication records of 236 Queensland independent and non-government schools. 81% publish a DMARC record, but only 51% enforce it and 19% have none at all — a gap that matters more since the 2026 Canvas incident put school contact lists in criminal hands.
Read update
10 August 2026
Queensland's $11.5 million micro-credentials program: free cyber security, AI and procurement training for small business
A new $11.5 million Queensland Government investment funds free AI, cyber security and procurement micro-credentials for small and family businesses through the University of the Sunshine Coast. A separate, already-available free cyber security course runs through TAFE Queensland. Neither replaces a proper security review, but both are a genuinely useful, no-cost starting point.
Read update
6 August 2026
School boards and the cyber storm: what ASD's frontier AI guidance means for education governance
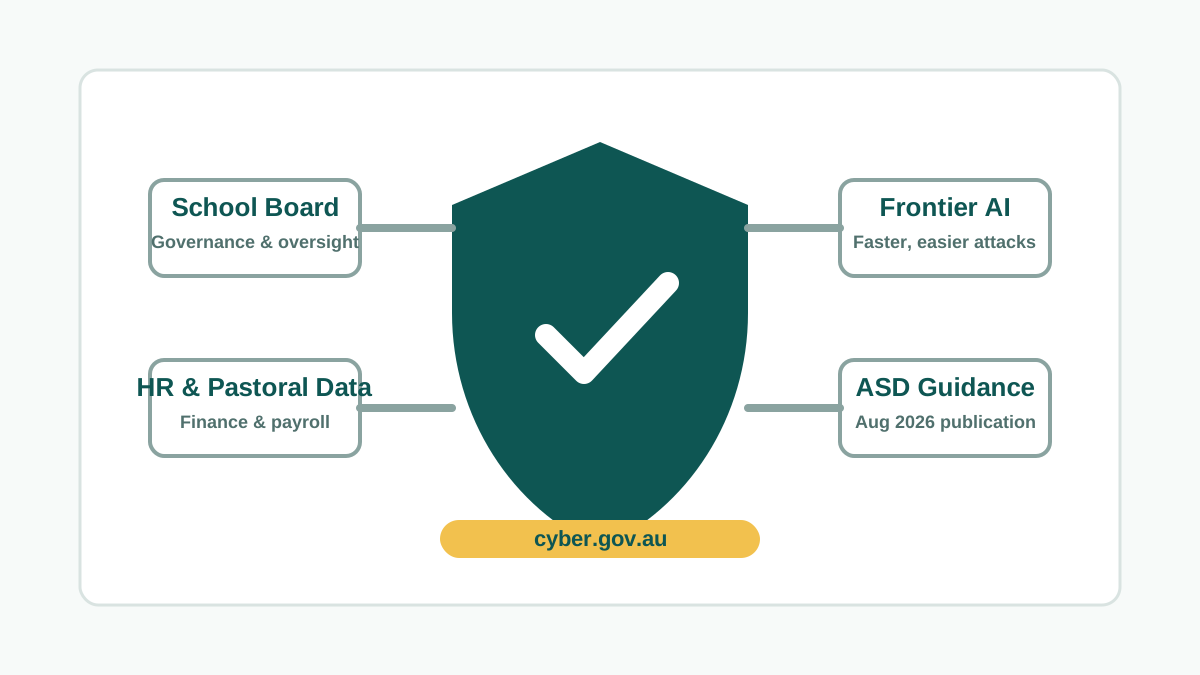
Australian school boards hold some of the most sensitive data in the community — HR, finance and pastoral care records — yet cyber is rarely a standing board agenda item. ASD's new frontier AI guidance for directors is a practical prompt to change that.
Read update
29 July 2026
What a Queensland Audit Office report on third-party cyber risk means for the rest of us
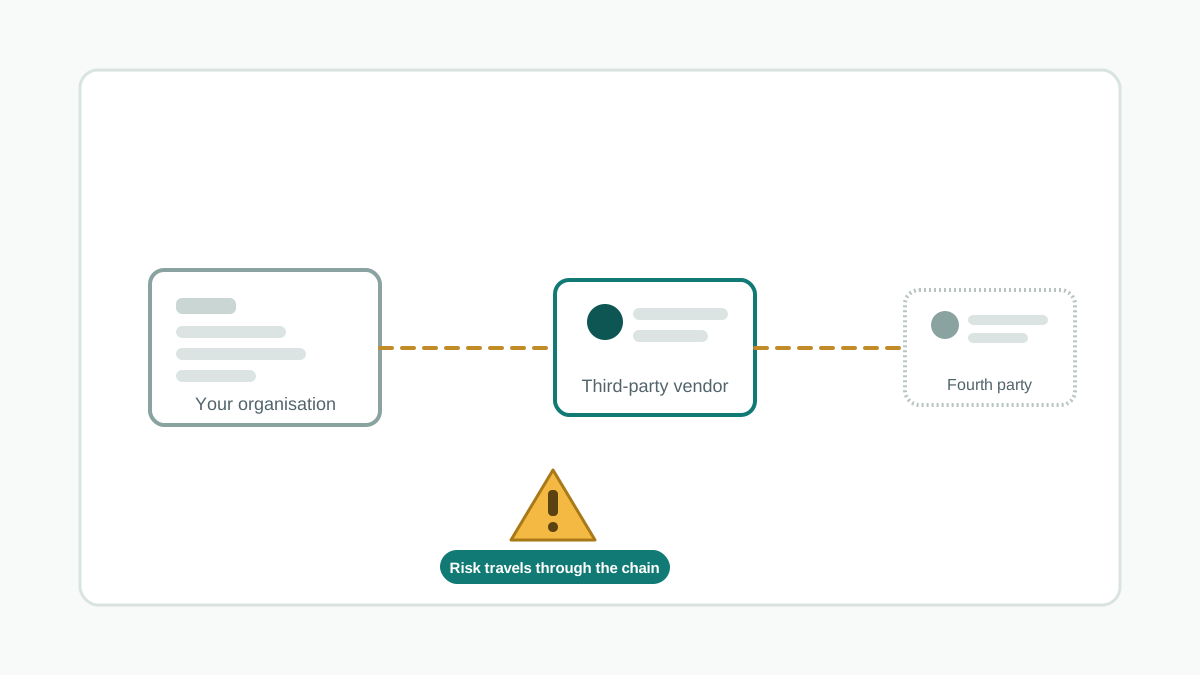
The Queensland Audit Office's Managing third-party cyber security risks report found public sector entities gave testers admin-level access and left security out of most vendor contracts. Here's what smaller organisations can take from it.
Read update
28 July 2026
Australia's Cyber Security Strategy 2023–2030: the six shields, in plain English
Australia's national cyber security strategy is built around six "cyber shields" and three delivery horizons running to 2030. Here's what each shield actually means, without the policy-document language.
Read update
28 July 2026
The Department of Home Affairs, the Cyber Security Act 2024, and what it actually means for a small organisation
Australia's first standalone cyber security law introduced mandatory ransomware payment reporting, a no-fault incident review board and new device security standards. Most small businesses and charities aren't directly captured — but the direction of travel matters.
Read update
28 July 2026
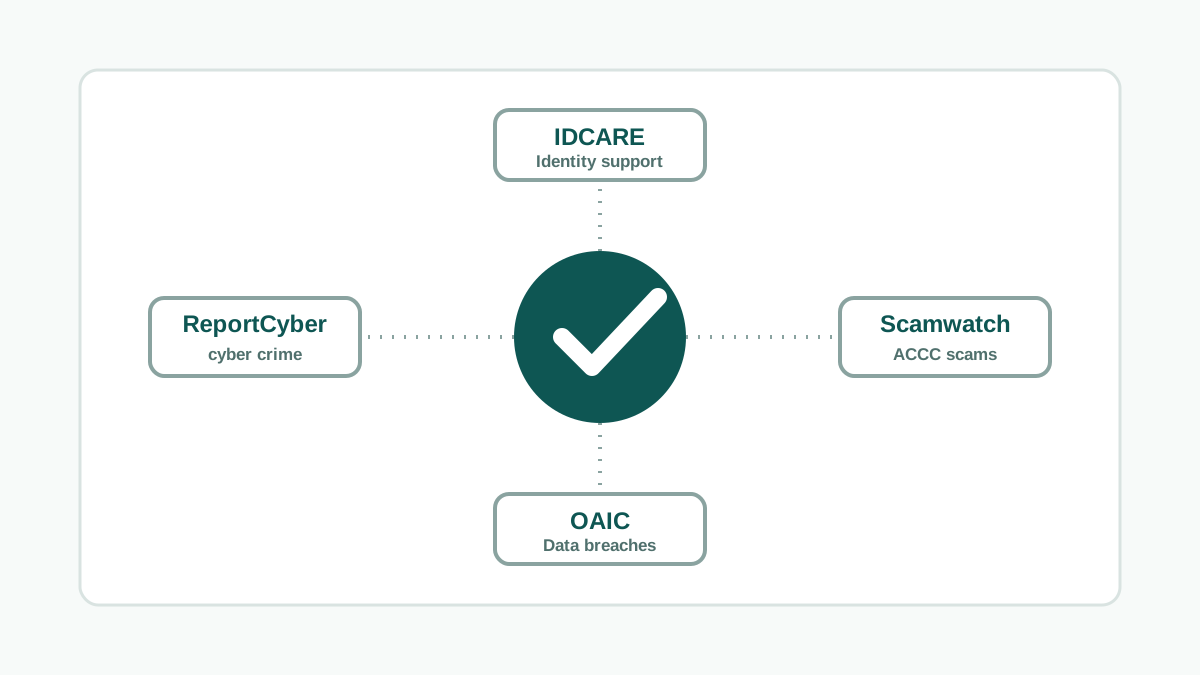
Who do you actually call? Cyber incident and scam reporting in Australia, decoded
ReportCyber, Scamwatch, IDCARE, the OAIC, eSafety — Australia has several different reporting agencies depending on what's actually happened. Here's which one to use, in plain English.
Read update
28 July 2026
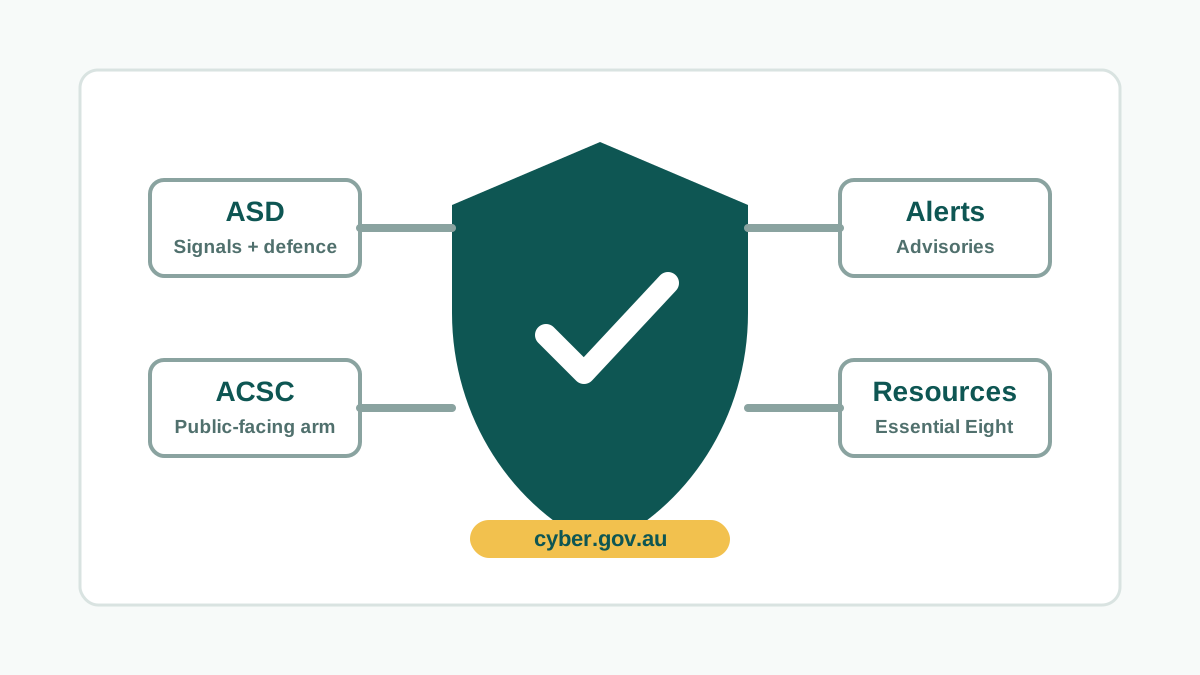
ASD and ACSC explained: who actually protects Australian businesses online
The Australian Signals Directorate and the Australian Cyber Security Centre are often mentioned in the same breath, but they're not quite the same thing. Here's what each one actually does, in plain English.
Read update
30 June 2026
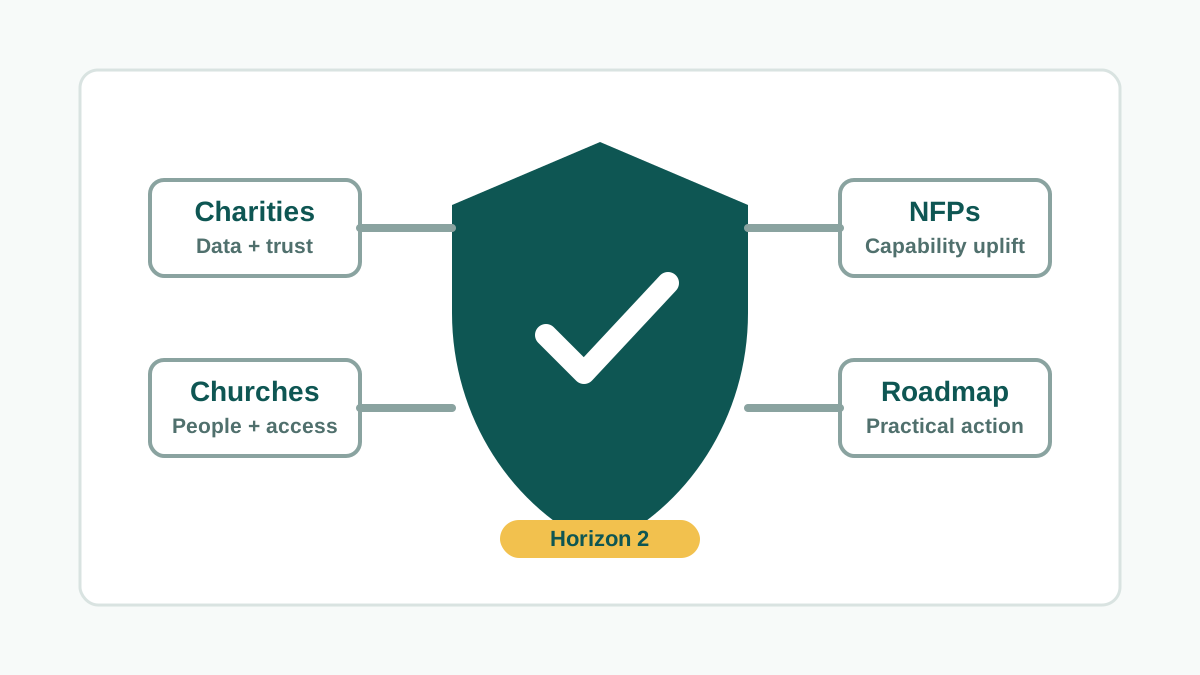
NFPs named in Australia’s next cyber security action plan
Australia’s Horizon 2 cyber security plan includes specific action for charities and not-for-profits. That is a useful signal for boards, church leaders and community organisations.
Read update